Logging into a personal account at Bizzo Casino requires more than simply typing a username and password set https://bizzo.com.nl/login/. Every completed authentication attempt, failed login, password reset, and critical account update is methodically documented on the platform’s backend. Comprehending how to navigate and understand the login history and activity log functions as a basic practice for preserving strict account hygiene. This record offers a open audit trail that allows users to verify that no illegitimate party has tried to breach their account information or manipulate their ongoing session while actual cash balances and confidential personal data remain secured behind the platform’s encryption protocols.
Table of Contents
Registering Your Bizzo Casino Account Safely
The journey toward a comprehensive activity log commences with a carefully completed registration. A fresh registrant should click the sign-up button and enter precise personal details such as a full legal name, a valid email address, and a mobile phone number. The system checks this data during the initial validation phase. Submitting falsified details during this step will certainly create friction later when the withdrawal team demands identity verification documents. A unique password combining uppercase letters, numeric values, and special characters needs to be generated to create the first marker in what will become a comprehensive historical record of account interactions tracked by the server.
Upon filing the registration form, the platform dispatches a verification link or a one-time code to the provided contact channel. Enabling the account through this confirmation step is required and functions as the first manual approval in the user’s lifecycle timeline. Without accessing the activation email, the profile persists in a suspended state and cannot accept deposits. This initial handshake confirms that the email address is associated with the user and captures the exact timestamp of confirmation. Finishing this step populates the nascent activity log with the registration IP address, device type, and browser fingerprint, creating a baseline profile for future security correlation checks.
Exploring the Authentication Interface Efficiently
The sign-in portal is designed with a simple aesthetic to reduce cognitive load, showing only the essential email and password fields on the initial interface. A member returning to the site should personally type the intended URL or use a stored bookmark to bypass phishing domains that imitate the branding. Once the credentials are typed, the system computes a cryptographic hash of the password to compare against the saved database record without transmitting the secret in plain text. The interface features a toggle option to show the typed password, a function handy for mobile users whose keyboards may introduce capitalization errors. Successful authentication unlocks the entry to the personal cabinet.
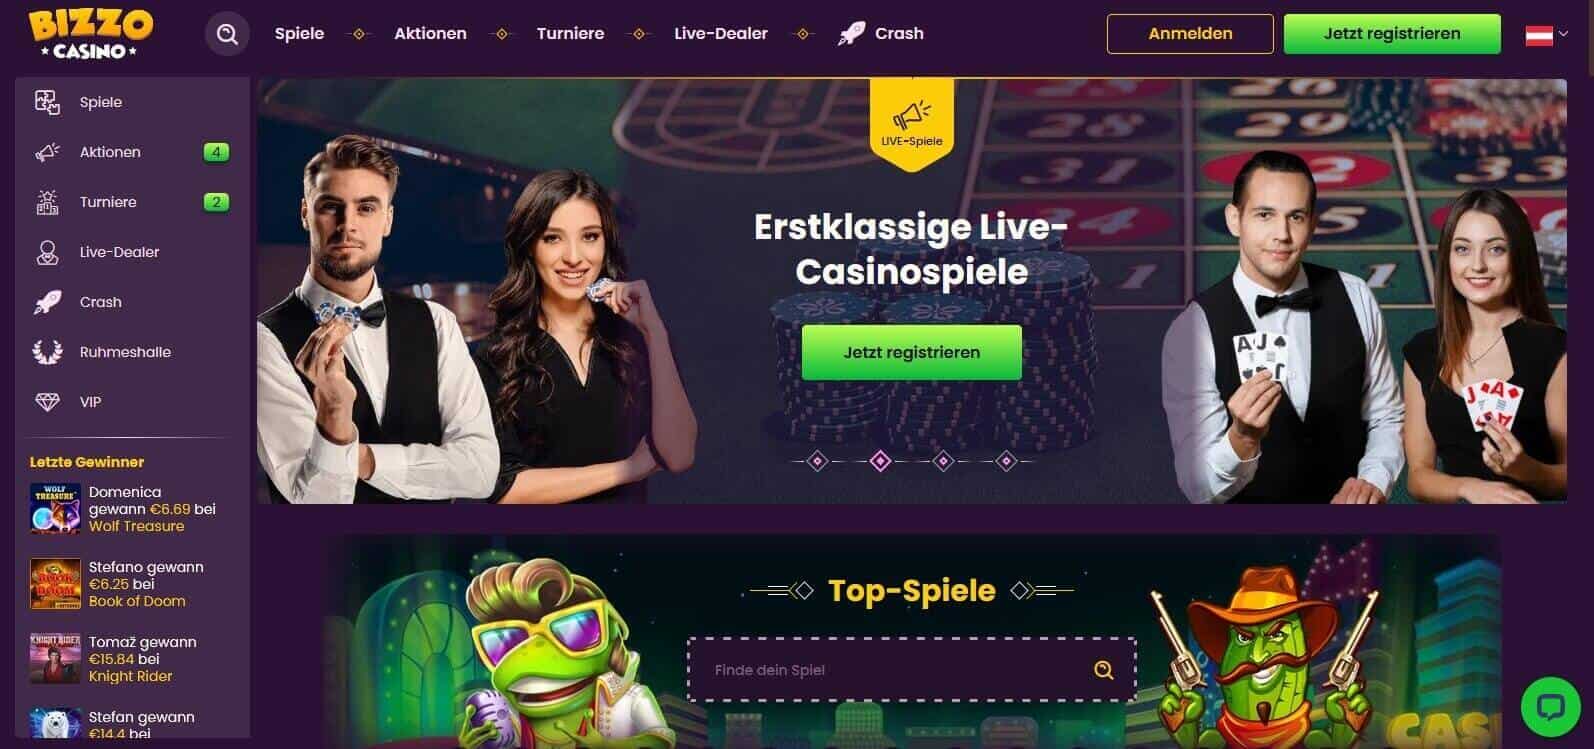
Directly beneath the form fields, a “Forgot Password” recovery link is placed. If a session times out because of extended inactivity, the system sends automatically back to this gateway, requesting a fresh sign-in. The login page also identifies whether a user is connecting from a formerly recognized device. If the digital fingerprint is unfamiliar, an adaptive risk engine may activate an additional verification step before allowing entry. This silent analysis occurs within milliseconds and directly adds a device recognition entry into the activity log, marking the event as a routine authentication or a high-risk anomaly worth reviewing later.
Setting up Two-Factor Authentication for Enhanced Log Integrity
Two-factor authentication incorporates a cryptographic time-based one-time password layer that transforms how login history entries are classified. Activating this feature within the safety settings forces the server to demand a secondary token after the primary password validates successfully. The activity log then records a two-stage event chain, where a correct password but a missing or late token generates an “Incomplete 2FA” flag. This distinction is vital because it proves the primary credential was exposed yet the secondary barrier stayed secure, giving the genuine owner time to reset the password before a full perimeter breach happens.
Setting up two-factor authentication requires scanning a QR code with an authenticator application or enrolling a hardware security key. Once set up, the login log will display a lock icon next to authenticated sessions, confirming the session was secured. A user can review past entries to confirm no session circumvented the second factor. In the rare event of a phone theft or authenticator app failure, the stored backup recovery codes become the sole override method. The utilization of any single backup code is recorded as a high-severity event in the log, recording the exact date and time the emergency recovery channel was used.
Deciphering the Dashboard Activity Stream
Inside the account cabinet, the activity log is presented as a chronological stream of events, not as a static unchangeable list. Each row constitutes a discrete action and carries a precise UTC timestamp down to the second, a classification tag, and a truncated IP address for privacy compliance. The interface enables a player to filter the feed by date range or by specific action categories. Users watching their security posture closely can isolate “Authentication” events to see every login attempt from the last thirty days. This tool eradicates the guesswork often associated with shared devices or public Wi-Fi usage and brings total transparency.
An entry marked “Login Successful” records the browser version and operating system. If a rival entry appears marked “Login Failed” with an unrecognized geographic indicator, the account holder obtains an immediate signal that a credential-stuffing bot may be targeting their email. The log also records sensitive administrative actions such as updating a linked phone number or modifying the primary email. Any alteration to the account’s fundamental identity structure is permanently inscribed here, offering a forensic trail. Regularly scanning this stream transforms a passive user into an active guardian of their own digital funds and personal data integrity.
Observing Device and Session History
Past the chronological event stream, a dedicated session management panel presents currently active and recently terminated sessions. Each logged-in instance bears a descriptive label specifying the device model, the browser engine, and the approximate location based on network mapping. If a user logs in from a desktop in Amsterdam and later spots a concurrent mobile session active from a different continent, the timeline uncovers the intrusion instantly. The interface provides a one-click termination button to remotely log out a suspicious session. Terminating a rogue session instantly cancels the authentication token, forcing the intruder to re-authenticate, a feat impossible without the updated credentials or second factor.
An exhaustive list of previously authorized devices lives within this module. Users often grant “Remember This Device” permission on personal laptops, thereby adding a persistent token to the system. The activity log notes each remembered device’s creation date and last use. If a device is lost or sold, removing its trusted status from this panel nullifies the stored token without requiring a full password reset. This granular control expands the security perimeter beyond mere password strength. By cross-referencing the device list with the login log, a player can recognize whether an old, forgotten tablet still holds an active authorization key to the account.
Validating Account Documentation and Identity Checks

The Know Your Customer procedure aligns tightly with the activity timeline, leaving audit entries that a careful user can track. When a withdrawal triggers a verification request, the system prompts an upload for a government-issued photo ID, a recent utility bill, and potentially a front-and-back photograph of the payment card used for deposits. Each upload attempt is recorded whether approved or rejected. A rejection entry in the activity feed explains the precise reason, such as a blurry image or an expired document, allowing the user to rectify the issue swiftly. Absence of these log entries suggests the documentation queue has not yet been processed.
A fully verified account status unlocks unrestricted access to the cashier. The log marks a “Documents Approved” milestone, effectively upgrading the trust tier internally. From this point forward, any request to change the registered home address requires a fresh re-verification, a change that itself is logged and flagged for manual compliance review. For players who value transparency, this integration means that the status of a payment hold is never a mystery. They can see precisely where they are in the verification pipeline. The immutable nature of these compliance logs safeguards both the operator and the user in case of future disputes.
Auditing Financial Transactions Within the Log
The activity tracker reaches its reach deep into the cashier module, efficiently merging security events with financial state changes. A deposit request triggered via iDEAL or an e-wallet generates a pending transaction marker. When the funds settle and become available in the casino wallet, the log records a success event accompanied by a unique transaction hash. Should a deposit timeout or fail due to insufficient bank balance, a distinct failure entry appears. This granularity assures that a player never needs to chase support for a basic status update. The answer to where funds are located is always displayed clearly in the chronological feed for immediate reference.
Withdrawal requests go through an even more detailed documentation process. The log records the request submission, the internal queue position, the compliance review outcome, the payment processing timestamp, and the final completion notice. Any cancellation of a pending withdrawal by the player while it is in the reversible queue also receives its own log line. This transparency removes the anxiety often associated with waiting for payouts. By scrolling through the transaction history alongside the login history, an account holder can connect large payouts with specific session timestamps, verifying that no financial action occurred outside of their remembered active login sessions.
Maintaining a routine of reviewing the login history and activity log transforms account maintenance into a proactive defense mechanism rather than a reactive scramble after noticing missing funds. The wealth of timestamped data, from registration verification through two-factor challenges to final withdrawal settlements, delivers a full narrative of account ownership. Bizzo Casino provides the instrumentation necessary to audit every digital interaction, and the vigilant player who leverages these tools builds a fortress-like posture around their entertainment budget. Reading the log quarterly, if not monthly, stays a minimal investment for maximum account integrity.
 दिनभर की ख़बरों का बंदोबस्त. बनारस की बात. फिल्मों के किस्से, इतिहास-स्पोर्ट्स-राजनीति का माहौल. देश-दुनिया, अर्थव्यवस्था, साइंस की अनोखी बातें और विडियोज सिर्फ बनारस टुडे पर.